

GDPR Email Signature
Create a compliant email signature that meets GDPR standards effortlessly.
What is a GDPR Email Signature?
A GDPR email signature is a digital signature that complies with the General Data Protection Regulation (GDPR) standards. This type of signature ensures that your email communications respect the privacy rights of individuals. For businesses, having a GDPR compliant email signature is crucial as it reflects a commitment to data protection and privacy. Non-compliance can lead to significant legal implications, including hefty fines and damage to your reputation.
Why You Need a GDPR Compliant Signature
Having a GDPR compliant email signature is essential for several reasons. First, the consequences of non-compliance can be severe, including financial penalties and legal action. Second, using compliant signatures offers benefits such as increased trust with clients, as it demonstrates your commitment to protecting their personal information. Lastly, a well-crafted signature can enhance your professional image and credibility in business communications.
Steps to Create a GDPR Email Signature
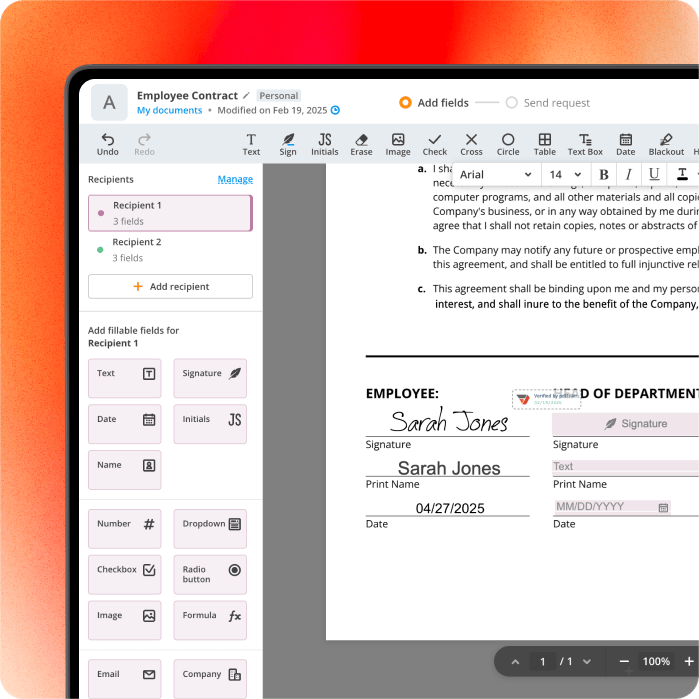
- Access the signature tool provided by pdfFiller to start creating your GDPR email signature.
- Choose the appropriate signature format that aligns with your business needs.
- Add necessary information such as your name, position, company name, and contact details.
- Include a disclaimer about data protection and privacy in your signature.
- Ensure that your signature is visually appealing and professional.
- Review the signature for compliance with GDPR requirements.
- Save your signature and prepare to integrate it into your email client.
Customizing Your GDPR Email Signature
Personalizing your email signature can make it more engaging. Start by choosing fonts and colors that reflect your brand identity. Adding logos and images can enhance recognition, but ensure they do not compromise readability. Keeping your signature clear and concise is vital for effective communication.
Legal Validity of Your Signature
Your GDPR email signature must comply with regulations to be legally valid. This includes maintaining audit trails and timestamps that can verify the authenticity of the signature. Understanding the legally binding aspects of your email signature is crucial, as it can protect your business in case of disputes.
Common Mistakes to Avoid
When creating your GDPR email signature, avoid common pitfalls such as omitting necessary information like your contact details or privacy disclaimers. Using non-compliant designs can also lead to issues, so ensure your signature meets all legal requirements. Additionally, ignoring mobile compatibility can result in a poor user experience for recipients viewing your emails on mobile devices.
Examples of GDPR Email Signatures
- A simple, text-based signature that includes essential contact information and a GDPR disclaimer.
- A professional signature for freelancers that showcases their logo and includes links to their website and social media.
- An industry-specific signature for small businesses that highlights compliance-focused designs and relevant certifications.
Integrating Your Signature with Email Clients
- Follow the instructions for adding your signature to popular email clients like Outlook, Gmail, and Apple Mail.
- Check compatibility tips to ensure your signature displays correctly across different platforms.
- Test your signature by sending emails to yourself and others to confirm it appears as intended.
Next Steps After Creating Your Signature
After creating your GDPR email signature, test it for compliance to ensure it meets all necessary standards. Share the signature with team members to maintain consistency in communications. Regularly update your signature as needed to reflect any changes in your contact information or business details.