
Last updated on
Oct 31, 2026
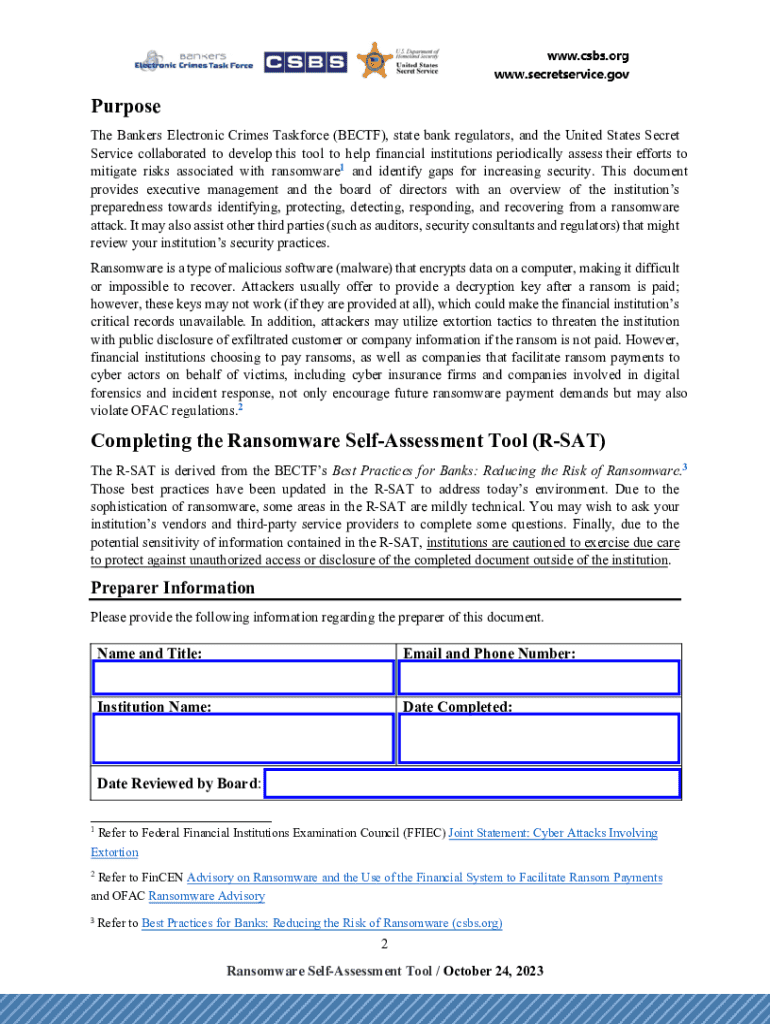
Get the free Ransomware Self-Assessment Tool
We are not affiliated with any brand or entity on this form

Fill out
Complete the form online in a simple drag-and-drop editor.

eSign
Add your legally binding signature or send the form for signing.

Share
Share the form via a link, letting anyone fill it out from any device.

Export
Download, print, email, or move the form to your cloud storage.
Why pdfFiller is the best tool for your documents and forms


End-to-end document management
From editing and signing to collaboration and tracking, pdfFiller has everything you need to get your documents done quickly and efficiently.
Accessible from anywhere
pdfFiller is fully cloud-based. This means you can edit, sign, and share documents from anywhere using your computer, smartphone, or tablet.
Secure and compliant
pdfFiller lets you securely manage documents following global laws like ESIGN, CCPA, and GDPR. It's also HIPAA and SOC 2 compliant.
What is R-SAT Tool
The Ransomware Self-Assessment Tool is a service agreement used by financial institutions to assess and enhance their ransomware risk mitigation efforts.
pdfFiller scores top ratings on review platforms




Who needs R-SAT Tool?
Explore how professionals across industries use pdfFiller.

R-SAT Tool is needed by:
-
Executive management in financial institutions
-
Board of directors overseeing cybersecurity
-
Auditors evaluating risk management practices
-
Security consultants advising on ransomware preparedness
-
State bank regulators monitoring compliance
-
Cyber insurance providers assessing client risk
Comprehensive Guide to R-SAT Tool
What is the Ransomware Self-Assessment Tool?
The Ransomware Self-Assessment Tool (R-SAT) serves as a foundational resource for financial institutions aiming to evaluate their preparedness against ransomware attacks. Developed collaboratively by multiple regulatory bodies, including the Bankers Electronic Crimes Task Force, the tool is a pivotal element in identifying and managing ransomware risks within the financial sector.
Version 2.0 of R-SAT emphasizes the necessity for financial institutions to thoroughly assess their resilience against ransomware threats. Understanding these risks is critical for banks and credit unions, allowing them to take proactive measures in their cybersecurity strategies.
Purpose and Benefits of the Ransomware Self-Assessment Tool
The primary purpose of the Ransomware Self-Assessment Tool is to enhance organizations' cybersecurity measures effectively. By utilizing this tool, institutions can identify gaps in their ransomware risk mitigation strategies, thereby strengthening their defenses.
Additionally, it facilitates essential discussions among executive management, board members, and auditors, fostering a culture of awareness regarding ransomware preparedness within the organization.
Key Features of the Ransomware Self-Assessment Tool
The Ransomware Self-Assessment Tool is equipped with distinct features that enhance its usability. Users will find checkboxes for quick assessments, fillable fields for specific information, and a user-friendly format designed for easy navigation.
Moreover, the tool aligns with the FFIEC cybersecurity framework, ensuring a comprehensive evaluation of the financial institution's cybersecurity posture. This alignment ensures that institutions can confidently assess their ransomware preparedness.
Who Needs the Ransomware Self-Assessment Tool?
The target audience for the Ransomware Self-Assessment Tool includes executive management, board directors, and third-party auditors. These stakeholders play a vital role in overseeing the cybersecurity measures within financial institutions.
Whether for banks or credit unions, understanding the importance of the tool is essential for enhancing overall cybersecurity and compliance within the financial sector.
How to Fill Out the Ransomware Self-Assessment Tool Online (Step-by-Step)
-
Access the online form through the designated platform.
-
Begin by filling in basic information such as 'Name and Title' and 'Email and Phone Number.'
-
Proceed to evaluate the various sections, using checkboxes to indicate responses.
-
Complete each section thoroughly, ensuring all required fields are filled out.
-
Review the completed form to avoid any errors before submission.
Common Errors and How to Avoid Them
When completing the Ransomware Self-Assessment Tool, users may encounter common errors, such as leaving mandatory fields blank or providing incorrect information. Addressing these issues is crucial to ensure valid assessments.
To mitigate such errors, validating information before submission is essential. Users should take care to double-check entries and be mindful of any prompts indicating missed fields.
Security and Compliance for Handling the Ransomware Self-Assessment Tool
Security is a paramount consideration when using the Ransomware Self-Assessment Tool. pdfFiller employs robust security features, including 256-bit encryption, ensuring that sensitive information is protected throughout the assessment process. Compliance with HIPAA and GDPR further safeguards user data.
Understanding these security measures is vital for users concerned about the safety of their information during and after using the tool.
How to Submit the Ransomware Self-Assessment Tool
Submission methods for the Ransomware Self-Assessment Tool are versatile, including options such as email or direct submission via an online platform. Institutions should choose the method that best fits their operational procedures.
Upon submission, users can expect a timeline for processing their assessments, along with confirmation details to ensure that the submission was successful.
What Happens After You Submit the Ransomware Self-Assessment Tool?
After submitting the Ransomware Self-Assessment Tool, the evaluation processes will commence, as regulatory bodies review the submitted information. Institutions should expect potential follow-ups for additional details or clarifications.
Maintaining accurate records of submissions is crucial for compliance with regulations, ensuring that financial institutions are prepared for any future audits or assessments.
Empower Your Financial Institution with pdfFiller
Utilizing pdfFiller for form management streamlines the process of completing the Ransomware Self-Assessment Tool. Its intuitive interface allows users to efficiently edit and manage documents.
Additional features, such as eSigning and document sharing, further enhance organizational efficiency, making it easier for institutions to work collaboratively and ensure robust ransomware preparedness.
How to fill out the R-SAT Tool
-
1.Access pdfFiller and search for the Ransomware Self-Assessment Tool by typing its name in the search bar.
-
2.Open the form by clicking on it in the search results to launch the editable document.
-
3.Familiarize yourself with the layout of the form, noting areas with checkboxes and fillable fields.
-
4.Gather necessary information such as your institution's ransomware policies, previous cybersecurity audits, and relevant contacts before completing the form.
-
5.Begin by marking the appropriate checkboxes for the questions presented in the form. Utilize '☐ YES' or '☐ NO' options as needed.
-
6.Fill in the fields for 'Name and Title', 'Email and Phone Number', and any other requests for information, ensuring accuracy.
-
7.If required, include additional notes in available blank lines to provide more details relevant to your assessment.
-
8.Once all sections are completed, review the form for any missing information or errors.
-
9.Utilize pdfFiller's review tools to make amendments and finalize the document.
-
10.When satisfied with your entries, save the changes to ensure your work is secured.
-
11.Choose to download the filled form or submit it directly through pdfFiller's submission options, following their prompts for completion.

Who is eligible to use the Ransomware Self-Assessment Tool?
The Ransomware Self-Assessment Tool is intended for financial institutions, particularly those involved in managing bank cybersecurity and risk assessment. It is suitable for executive management, board members, and regulatory auditors.
Is there a deadline for completing the assessment using this tool?
While there are no specific deadlines stated for using the Ransomware Self-Assessment Tool, it is advisable to complete the assessment during periodic reviews of your cybersecurity measures to maintain effective ransomware preparedness.
How do I submit the completed form?
After filling out the Ransomware Self-Assessment Tool on pdfFiller, you can submit it directly through the platform's submission options or download it for your records or to send via email.
Are there any supporting documents required with this tool?
While the Ransomware Self-Assessment Tool does not require additional supporting documents, it is beneficial to have previous cybersecurity audits or risk assessments available for reference while completing the form.
What common mistakes should I avoid when filling out this tool?
Common mistakes include neglecting to thoroughly review each section and omitting information in the fillable fields. Ensure all checkboxes are answered and double-check contact details before saving or submitting.
How long does it take to process the information collected in this assessment?
Processing time for the completion of this assessment depends on the complexity of your institution's cybersecurity posture, but typically, filling out the Ransomware Self-Assessment Tool should take 30 to 60 minutes.
What if I have questions while completing the Ransomware Self-Assessment Tool?
If questions arise while completing the Ransomware Self-Assessment Tool, consult your IT security team or a cybersecurity consultant for assistance in addressing technical inquiries and providing clarity on the assessment points.
Related Forms





Get the latest insights from our blog



If you believe that this page should be taken down, please follow our DMCA take down process
here
.
This form may include fields for payment information. Data entered in these fields is not covered by PCI DSS compliance.