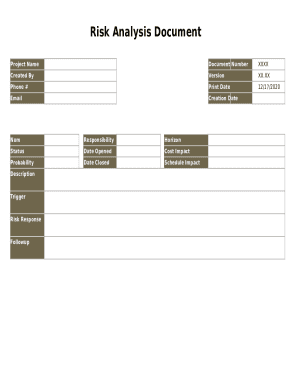
What is Risk Analysis Document?

A Risk Analysis Document is a comprehensive report that identifies, assesses, and evaluates potential risks that may impact a project, business, or organization. It outlines the potential threats, their likelihood of occurrence, and the potential consequences they may have.

What are the types of Risk Analysis Document?

There are several types of Risk Analysis Documents that can be used depending on the nature of the project or business. Some common types include:

Qualitative Risk Analysis Document
Quantitative Risk Analysis Document
Strategic Risk Analysis Document

How to complete Risk Analysis Document

Completing a Risk Analysis Document requires careful consideration and thorough analysis. Here are some steps to guide you through the process:

01
Identify potential risks and threats
02
Assess the likelihood and impact of each risk
03
Develop mitigation strategies to address the risks
04
Monitor and review the effectiveness of the mitigation strategies

pdfFiller empowers users to create, edit, and share documents online. Offering unlimited fillable templates and powerful editing tools, pdfFiller is the only PDF editor users need to get their documents done.
Video Tutorial How to Fill Out Risk Analysis Document

Thousands of positive reviews can’t be wrong

Read more or give pdfFiller a try to experience the benefits for yourself
5.0
I liked the easy of using the Pdfiller and most importantly the added security c...
I liked the easy of using the Pdfiller and most importantly the added security code required before downloading the doc.
Gloria Oromu A
5.0
I really like this program.
I really like this program. It is easy to use, how ever it could simplify it's way of organizing pages. Overall, I like this tool.
Alexandra E
5.0
PDFfiller support team is very professional and quick to resolve issues in a tim...
PDFfiller support team is very professional and quick to resolve issues in a timely manner. Would definitely recommend this product.
Natalie T

Questions & answers

Your records should show that you: Conducted a good hazard review. Determined the risks of those hazards. Implemented control measures suitable for the risk. Reviewed and monitored all hazards in the workplace.
Step 1: Identify the hazards/risky activities. Step 2: Decide who might be harmed and how. Step 3: Evaluate the risks and decide on precautions. Step 4: Record your findings in a Risk Assessment and management plan, and implement them. Step 5: Review your assessment and update if necessary.
An IT risk analysis helps businesses identify, quantify and prioritize potential risks that could negatively affect the organization's operations. Examples of IT risks can include anything from security breaches and technical missteps to human errors and infrastructure failures.
Step 1) Hazard Identification. After determining an area to study, IDEM samples the affected environment, analyzes the samples, and identifies chemicals that may contribute to increased risk. Step 2) Exposure Assessment. Step 3) Dose-Response Assessment. Step 4) Risk Characterization.
You can do it yourself or appoint a competent person to help you. Identify hazards. Assess the risks. Control the risks. Record your findings. Review the controls.
Risk assessment is defined … as "A scientifically based process consisting of (i) hazard identification, (ii) hazard characterization, (iii) exposure assessment, and (iv) risk characterization."